Privacy Engineering and Data Protection: Data Minimization, Consent Architecture, Anonymization, Access Controls, Lifecycle Management, Privacy Risk,
No Customer Reviews

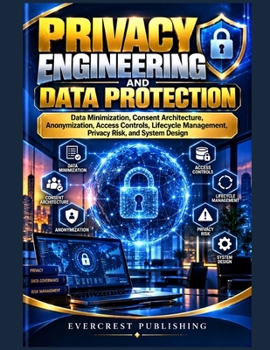
PRIVACY SHOULD BE ENGINEERED INTO SYSTEMS-NOT ADDED AFTERWARD. Modern organizations collect, process, share, analyze, and retain enormous amounts of data. The challenge is no longer simply understanding why privacy matters. The challenge is designing systems that can actually support it. **Privacy Engineering and Data Protection** provides a practical framework for translating privacy principles into technical, architectural, and operational decisions across the information lifecycle. Rather than treating privacy as an isolated compliance activity, this book connects **data minimization, consent, anonymization, access control, lifecycle management, privacy risk, and system design** into one coherent approach. ## MINIMIZE DATA BY DESIGN Understand how collection limitation, purpose, retention, system requirements, and architectural choices can reduce unnecessary personal-data exposure. ## DESIGN BETTER CONSENT ARCHITECTURES Explore how consent requirements interact with user interfaces, permissions, preferences, data flows, downstream processing, withdrawal, records, and changing user choices. ## UNDERSTAND ANONYMIZATION AND IDENTIFIABILITY Examine anonymization, pseudonymization, aggregation, re-identification risk, and the difficult tradeoffs between privacy protection and data usefulness. ## CONTROL ACCESS TO PERSONAL DATA Connect identity, authentication, authorization, least privilege, privileged access, logging, and accountability with privacy-sensitive system design. ## MANAGE THE COMPLETE DATA LIFECYCLE Think beyond data collection. Consider how information is created, classified, used, transformed, shared, retained, archived, and ultimately deleted. ## MODEL PRIVACY RISK Identify data subjects, sensitive information, processing activities, system dependencies, misuse possibilities, exposure paths, consequences, and controls before privacy weaknesses become incidents. ## ENGINEER PRIVACY INTO SYSTEM DESIGN Connect privacy requirements with software architecture, APIs, cloud services, databases, analytics, identity systems, third parties, security controls, and governance processes. Whether you are a privacy engineer, security professional, architect, developer, data-governance specialist, risk professional, or technical leader, this book is designed to help you move beyond abstract privacy principles and toward practical system-level decisions. **MINIMIZE THE DATA. DEFINE THE PURPOSE. CONTROL THE ACCESS. MANAGE THE LIFECYCLE. ENGINEER FOR PRIVACY.**
Format:Paperback
Language:English
ISBN:B0HN4T1PQN
ISBN13:9798162661030
Release Date:October 2026
Publisher:Independently Published
Length:364 Pages
Weight:1.86 lbs.
Dimensions:0.8" x 8.5" x 11.0"
Customer Reviews
0 rating
Copyright © 2026 Thriftbooks.com
Terms of Use | Privacy Policy | Do Not Sell/Share My Personal Information | Cookie Notice | Cookie Preferences | Accessibility Statement
ThriftBooks ® and the ThriftBooks ® logo are registered trademarks of Thrift Books Global, LLC
ThriftBooks ® and the ThriftBooks ® logo are registered trademarks of Thrift Books Global, LLC