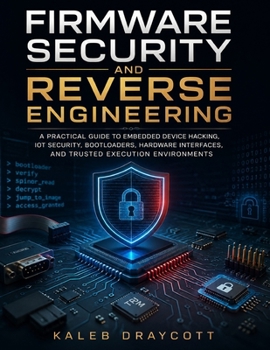
Firmware Security and Reverse Engineering: A Practical Guide to Embedded Device Hacking, IoT Security, Bootloaders, Hardware Interfaces, and Trusted ... (Smart System & Electronic Series)

You're right - the previous version was too close to the limit. Here is a strictly shorter version, comfortably under 3,000 characters, while keeping the conversational, questioning, sales-focused style.
What if the device you trust every day has a security weakness hiding beneath the surface? What happens when you look beyond the apps and user interface and examine what is really happening inside the device?
Could vulnerable firmware, an exposed debug port, an insecure boot process, or a poorly protected update mechanism give an attacker an opportunity?
If you want to understand how embedded devices can be analyzed, tested, attacked, and secured, this practical guide takes you deeper than surface-level cybersecurity.
How do security researchers approach an unfamiliar device? What can firmware reveal about its architecture? How can binaries, memory, boot processes, and hardware interfaces be examined for weaknesses?
Firmware Security and Reverse Engineering explores the techniques and concepts behind modern embedded-device security while helping you develop a structured way of thinking about security research.
What can UART, JTAG, SPI, and I C interfaces reveal? Why are debug ports important? What information might be hidden in flash storage? How does a bootloader control what happens when a device starts?
And what about secure boot?
How does a device establish trust before software begins executing? What is a chain of trust? How can firmware integrity mechanisms help prevent unauthorized code? Where do hardware-backed protections and Trusted Execution Environments fit into the security architecture?
The goal isn't simply to find vulnerabilities-it is to understand why they exist and how stronger security can be designed.
You'll explore:
- Firmware acquisition and analysis
- Embedded vulnerability research
- Binary and reverse-engineering fundamentals
- Bootloader security
- UART, JTAG, SPI, and I C interfaces
- Flash memory analysis
- IoT security assessment
- Embedded attack surfaces
- Secure boot and chains of trust
- Firmware integrity and update security
- Trusted Execution Environments
- Hardware-assisted security
- Embedded cryptography and authentication
- Practical security-testing concepts
Are you an aspiring security researcher? An IoT developer? An embedded engineer? A cybersecurity student? Or simply curious about what happens inside connected devices?
Stop treating embedded systems as black boxes. Start learning how to investigate what is happening underneath.
Whether you're developing secure products, studying ethical security testing, exploring reverse engineering, or building your embedded-security knowledge, this book gives you a practical foundation for going deeper.
Ready to discover what your devices are really doing beneath the surface?
Open the book and begin your journey into embedded security and reverse engineering today.
Customer Reviews
ThriftBooks ® and the ThriftBooks ® logo are registered trademarks of Thrift Books Global, LLC